
Changelog

Updates, changes, and improvements at Retool.

Refer to the stable and edge release notes for detailed information about self-hosted releases.

On September 30, 2026, Retool will conclude the public beta period for Assist and remove Assist from the classic app builder. All cloud and self-hosted instances will no longer be able to use Assist in the product.

The drag-and-drop experience for building and maintaining classic apps is still available. For an AI-powered building experience, Retool recommends using the new app builder. Converting your classic apps to the new app builder is free for Team, Business, and Enterprise organizations.

If you have any questions, reach out to the Community Forum or your account manager.

Enterprise organizations can use access policies to define which data each group of users can read or write on a resource. Retool enforces access policies on every query that runs against the resource. A policy can grant access to whole tables, specific columns, or specific rows.

For example, you can use an access policy to restrict an EMEA group's access on a table to only the customer rows for their own region. Retool applies that restriction to every query the group runs against the resource, so it holds regardless of which app, query, or agent the request comes from.

One policy covers queries from apps, the query library, raw SQL, and agents. Workflow queries against an enforced resource are blocked, so account for any workflows using the resource before you turn enforcement on. Retool supports access policies on PostgreSQL resources.

Access policies are enabled by default on cloud instances. On self-hosted instances, navigate to Settings > Beta and toggle on the feature flag for Enforce data security using access policies. To create a policy:

  1. Open a PostgreSQL resource and select the Access Enforcement tab.
  2. Turn on Data access enforcement.
  3. Create a policy, choose the groups and environments it covers, and define its rules.
  4. Activate the policy, then click Save changes.

Turning on data access enforcement closes the resource by default in every resource environment. Access policies apply only to the resource environments you select, so grant broad access first and narrow it once your policies are in place. Refer to Configure access policies for more details.

Access policies operate by granting access, not denying access. Refer to Access policies and Data access enforcement for more information.
You can now use Plan mode for further control over the actions that the app building agent takes.

  1. Click to switch from Build mode to Plan mode and tell the agent what changes you want it to make.
  2. The agent creates a comprehensive plan, which is written as a Markdown file in the .plan folder. Click Review to view the file.
  3. Review the plan, and switch to the Markdown tab to make any changes. You can also ask the agent to update the plan.
  4. When you're ready, click Build plan.

Retool is deprecating the dedicated Vertica resource type.

Retool will remove the resource type in Q1 2027, after two quarterly Stable releases. After removal, Vertica resources will stop working. Queries in apps and workflows that still point at those resources will fail. Retool will no longer ship the Vertica JDBC driver. Cloud organizations will not have a Vertica connection option after removal.

Self-hosted organizations can keep querying Vertica after removal by creating a JDBC resource and adding a Vertica JDBC driver that you provide. Retool will not migrate Vertica resources or their query references automatically.

  1. Download the Vertica JDBC driver from Vertica.
  2. Add the .jar file to your self-hosted instance. Follow the JDBC configuration steps for JDBC_DIRECTORY_PATH.
  3. Create a JDBC resource with Driver name com.vertica.jdbc.Driver, connection string jdbc:vertica://HOSTNAME:5433/DATABASE?user=USERNAME&password=PASSWORD&DisableCopyLocal=true, and schema query select table_name, column_name, data_type, table_schema from columns. Include DisableCopyLocal=true on the connection string.
  4. Open each app and workflow query that uses the Vertica resource. Change the query to use the new JDBC resource, then test it.

JDBC resources do not support Retool-managed SSH tunnels. If your Vertica resource uses an SSH tunnel, or you have a large number of Vertica queries and need help finding them, contact Retool Support.

Organization admins can now add shared building context that applies to all apps built with the new app builder. Building context is applied as custom instructions in the system prompt when the user makes any changes via prompting in the Chat tab, similar to the way AGENTS.md files work. Building context is valuable for defining design practices, coding conventions, data usage recommendations, and other guidelines across your organization.

To add shared context, navigate to Settings > Building context. Add your instructions in Markdown format, and click Publish to apply your changes to all apps.

Building context applies to all apps in your organization. If you have Spaces enabled, it applies to all apps in your space.

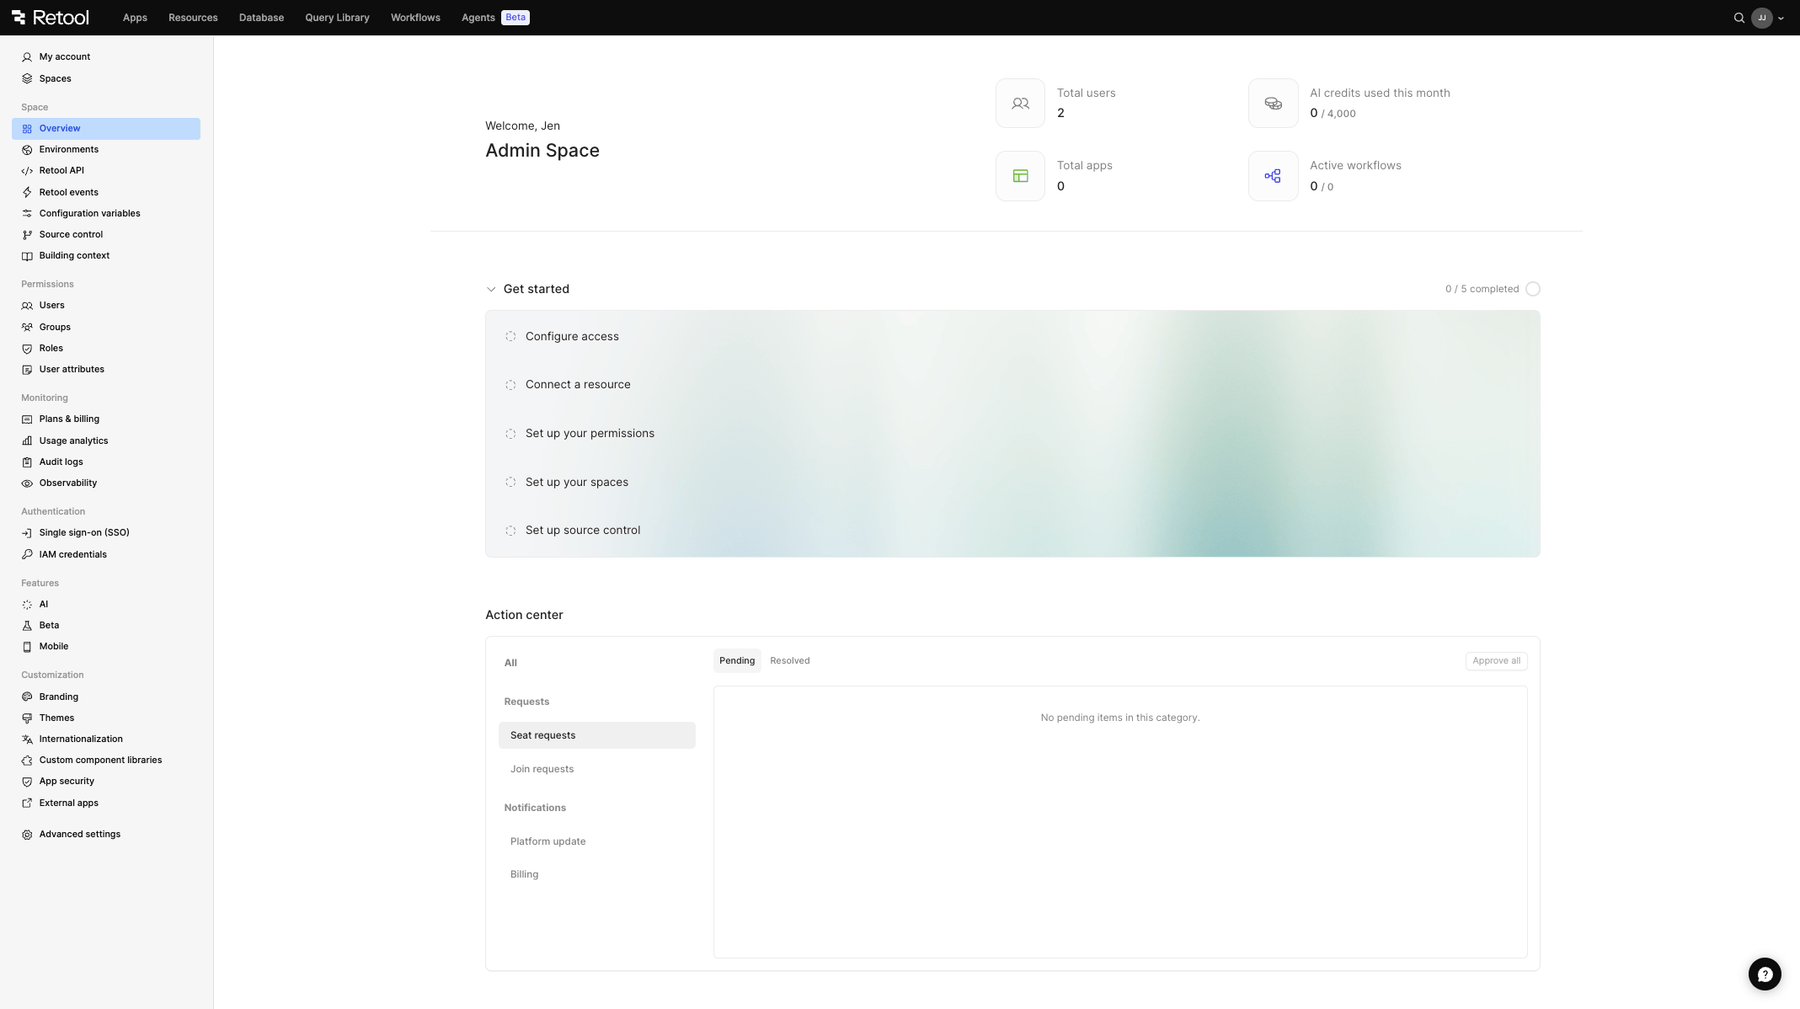
Admins on the Enterprise plan can now complete each step in the Get started section of the Overview page using guided step-by-step wizards instead of navigating through separate Settings pages to complete configuration.

Overview page

You can now directly configure from the Overview page:

  • SSO
  • Resources
  • Source control
  • Spaces
  • Permissions
note

The Permissions setup step is only available to organizations with object roles enabled. If object roles are not enabled for your organization, this step will be hidden. Refer to Object roles for more information.

The Get started section is aimed at providing a better onboarding experience for admins of new organizations, and will help identify what configurations still need to be set up for admins or existing organizations. For example, setting up spaces walks you through choosing custom spaces or a Dev/Staging/Prod environment split, naming and configuring each space, and optionally copying over your existing SSO settings, before creating every space at once.

The Overview page also includes an Action center that contains important notifications and pending join requests, suggested users, and seat upgrade requests, so admins can act on what needs attention, as well an at-a-glance overview of your organization stats, such as total users, apps, workflows, and AI credit usage.