
Changelog

Updates, changes, and improvements at Retool.

Refer to the stable and edge release notes for detailed information about self-hosted releases.

Buying additional AI credit packs by card is now available on all paid plans. Admins can buy a pack directly in Retool if their monthly allocation is running low.

To buy credits, go to Settings > Plans & Billing, select the AI Credits tab, then click Buy credits. Credits are available as soon as payment succeeds.
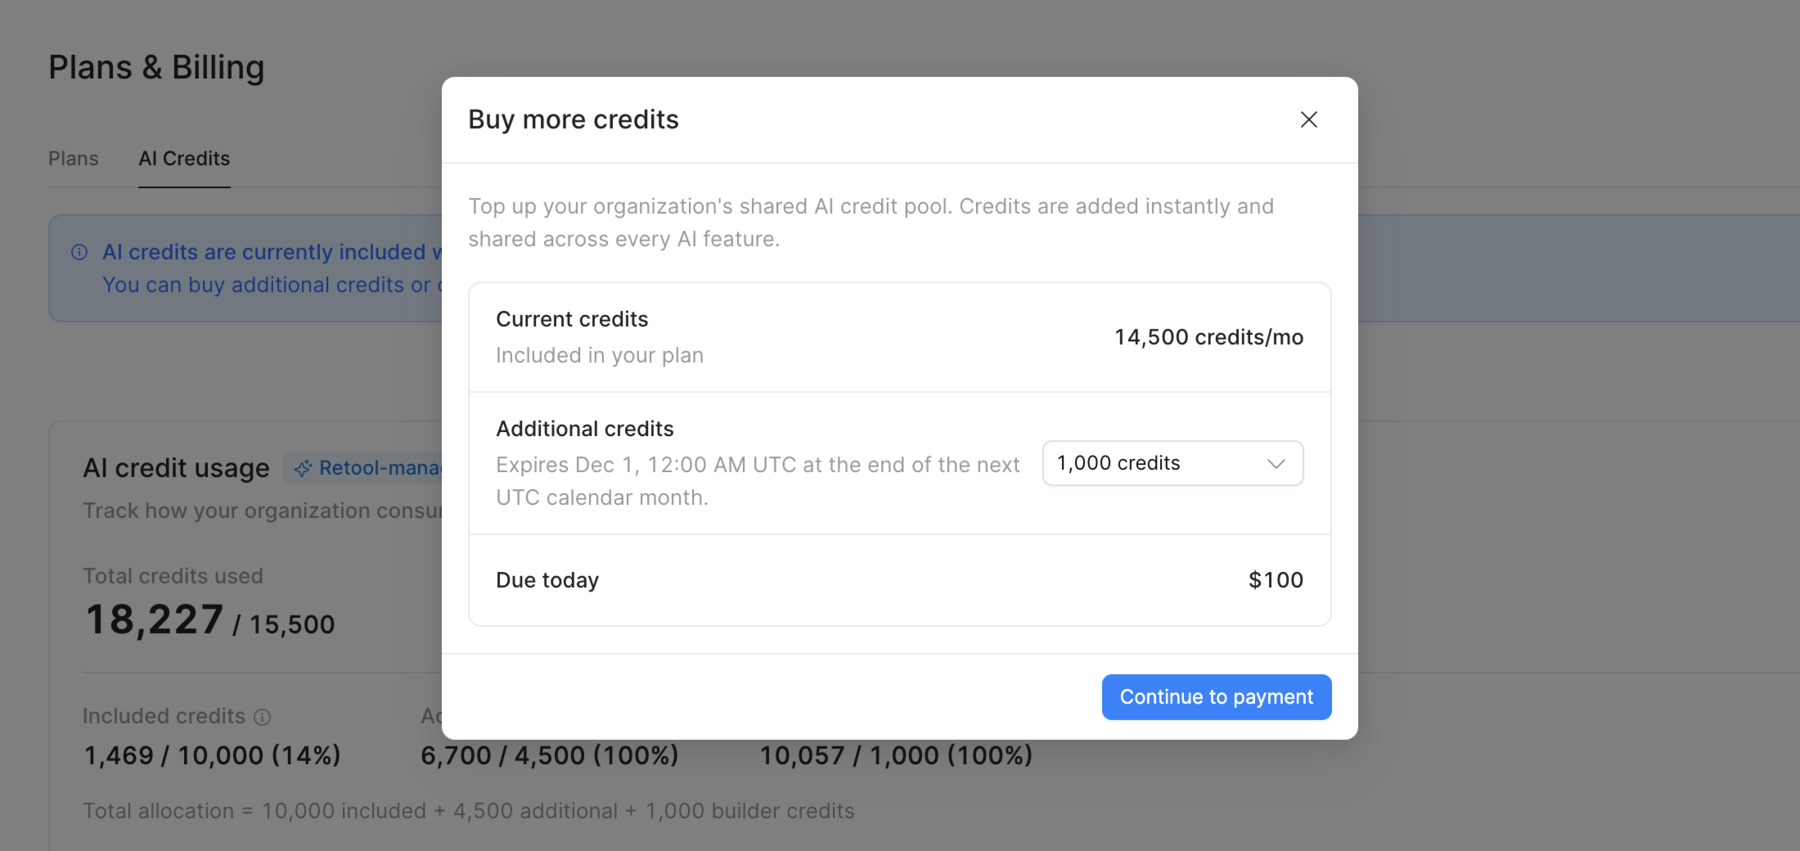
The Buy more credits dialog showing current credits, the credit pack selector, and the amount due today.

Purchased credits expire at the end of the next calendar month. For example, if you buy credits on October 20, they expire on November 30. On Enterprise plans with named seats, credits included with builder seats are used first. Then Retool uses your organization's monthly credits, then purchased credits.

The AI Credits tab also shows your additional AI credit history, including when each pack was added, how many credits remain, and when they expire.

Retool's AI-powered app builder is now generally available. Since first releasing the app builder in May 2026, Retool has continually expanded its capabilities to include:

Whatever or however you build, your apps inherit the security standards your organization has already approved and implemented.

To get started, admins can use the configuration guide to set up their organization to use the app builder.

note

Classic apps created with Retool's drag-and-drop IDE are still supported. While this experience continues to be maintained, Retool is focusing new feature development on the AI app builder.

Summary​

  • Several of eMudhra's emSign intermediate certificate authorities were compromised and revoked upstream. Components bundled in Retool trusted certificates signed by those intermediates.
  • This created a man-in-the-middle risk for self-hosted instances on affected versions: an attacker would need both a certificate from the compromised intermediates and a network position between your instance and an external endpoint.
  • Cloud was patched centrally. Self-hosted customers should upgrade.
  • IOCs: None. No exploitation observed, and no indication any maliciously signed package was pulled in.
  • Maintained stable releases contain a full fix (v4.0 and newer), version 3.334 received a partial fix for the Node, Python, and PIP systems, Java was not patched due to no upstream patch available.

A vulnerability in Node.js, the runtime that Retool runs on, can allow remote code execution. An out-of-bounds write in the Node.js Brotli decoder can be triggered by a crafted, Brotli-compressed HTTP response. Many of the HTTP clients that Retool uses decompress Brotli responses automatically. An attacker who can make a Retool instance send an HTTP request to a server they control, such as through a REST API resource, could use this to run code on that instance.