
Changelog

Updates, changes, and improvements at Retool.

Refer to the stable and edge release notes for detailed information about self-hosted releases.

38 posts tagged with "Enterprise"

Updates related to functionality on the Enterprise plan.

View All Tags

Expanded source control managers for multi-instance releases

Enterprise organizations can now implement multi-instance releases for apps using any supported SCM provider: AWS CodeCommit, Azure Repos, BitBucket, GitHub, and GitLab.

To enable multi-instance releases, navigate to Settings > Source control > Edit settings and turn on Enable multi-instance releases.

This feature enables you to publish different release versions across instances, making it possible to test a newer version on staging or development instances before promoting to production. Get started with multi-instance releases for apps.

Build resource environment switching for published apps

Organizations on paid plans can prompt the app building agent to use resource environments in published apps. Resource environments enable you to run a function against different configurations of the same resource, such as staging and production, and were previously only available in Edit mode for apps.

note

Published apps do not include an environment toggle by default.

Optionally, prompt the agent to add a UI element that allows app users to switch between resource environments.

When the user is not in the Finance Admin group, use the staging resource environment.
I want to use this app across resource environments. Add a dropdown in the top right corner.

In addition, you can use the _environment URL query parameter to open an app in a different environment, such as ?_environment=staging. This URL parameter works automatically and does not require prompting.

Custom authentication for embedded apps

Business and Enterprise organizations can now use the Retool API to authenticate apps that are embedded in an app or website external to Retool.

Once configured, the custom authentication flow exchanges an API token for an embed URL. When a parent app authenticates a user using your preferred authentication method, the parent app makes an API request to Retool to generate an embed URL. This embed URL is a secure, single-use link on the domain of your published app. Loading it in the iframe exchanges the link for a session, sets the cookies the app needs, and then displays the app.

Standard authentication through Retool remains supported.

note

This flow is available for apps published on a cloud instance that use the standard Retool domain (example.retool.com). It is not available to self-hosted instances or organizations that use a custom domain.

AI visibility for Enterprise

Retool introduced several features to help Enterprise organizations manage AI usage.

Use the new centralized settings page, AI visibility, to view AI credit usage and BYOK AI token usage. Navigate to Settings, and select Retool managed keys or Bring your own key from the dropdown at the top of the page. You can filter AI usage by instance, model, user, and feature.

note

This page is available on Enterprise plans. Admins can access it, and other users can access it with delegated Manage billing and Manage usage analytics permissions. Available views depend on the user’s permissions.

Enterprise organizations can also use the new Get AI credit usage endpoint to measure the number of credits consumed for each AI resource that uses a Retool-managed key. You can view the number of credits consumed by resource, user, and surface area.

Learn more about credit and token monitoring.

Multi-instance releases for apps

Multi-instance releases are now supported for apps built in the new app builder, in addition to classic apps and workflows. To enable multi-instance releases, navigate to Settings > Source control > Edit settings and turn on Enable multi-instance releases.

Organizations using Source Control can manage releases of protected apps, classic apps, and workflows across multiple deployment instances. This feature enables you to publish different release versions across instances, making it possible to test a newer version on staging or development instances before promoting to production.

note

At this time, GitHub is the only Source Control Manager (SCM) that is supported for apps. Others are being added.

Multi-instance releases work slightly differently for apps and classic apps. Learn more about the difference, or get started with multi-instance releases for apps.

Access policies for PostgreSQL resources in public beta

Enterprise organizations can use access policies to define which data each group of users can read or write on a resource. Retool enforces access policies on every query that runs against the resource. A policy can grant access to whole tables, specific columns, or specific rows.

For example, you can use an access policy to restrict an EMEA group's access on a table to only the customer rows for their own region. Retool applies that restriction to every query the group runs against the resource, so it holds regardless of which app, query, or agent the request comes from.

One policy covers queries from apps, the query library, raw SQL, and agents. Workflow queries against an enforced resource are blocked, so account for any workflows using the resource before you turn enforcement on. Retool supports access policies on PostgreSQL resources.

Access policies are enabled by default on cloud instances. On self-hosted instances, navigate to Settings > Beta and toggle on the feature flag for Enforce data security using access policies. To create a policy:

  1. Open a PostgreSQL resource and select the Access Enforcement tab.
  2. Turn on Data access enforcement.
  3. Create a policy, choose the groups and environments it covers, and define its rules.
  4. Activate the policy, then click Save changes.

Turning on data access enforcement closes the resource by default in every resource environment. Access policies apply only to the resource environments you select, so grant broad access first and narrow it once your policies are in place. Refer to Configure access policies for more details.

Access policies operate by granting access, not denying access. Refer to Access policies and Data access enforcement for more information.
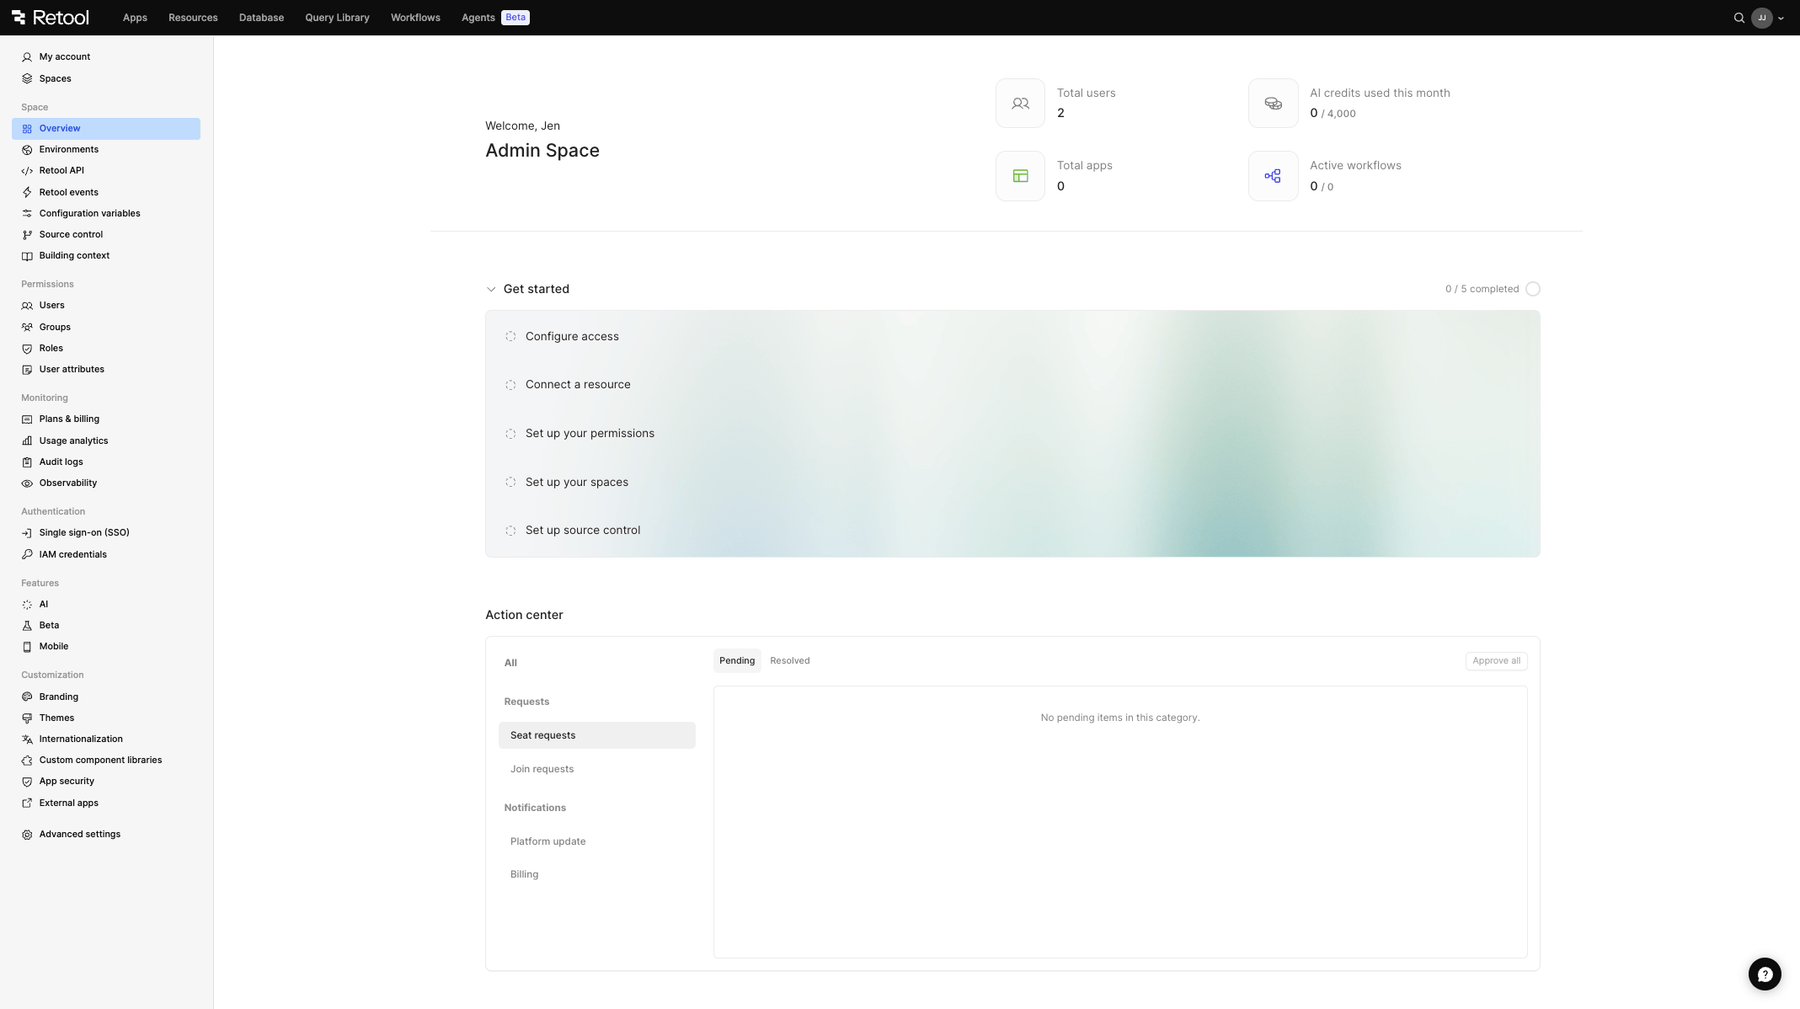
Admin onboarding hub now available in the Settings Overview page

Admins on the Enterprise plan can now complete each step in the Get started section of the Overview page using guided step-by-step wizards instead of navigating through separate Settings pages to complete configuration.

Overview page

You can now directly configure from the Overview page:

  • SSO
  • Resources
  • Source control
  • Spaces
  • Permissions
note

The Permissions setup step is only available to organizations with object roles enabled. If object roles are not enabled for your organization, this step will be hidden. Refer to Object roles for more information.

The Get started section is aimed at providing a better onboarding experience for admins of new organizations, and will help identify what configurations still need to be set up for admins or existing organizations. For example, setting up spaces walks you through choosing custom spaces or a Dev/Staging/Prod environment split, naming and configuring each space, and optionally copying over your existing SSO settings, before creating every space at once.

The Overview page also includes an Action center that contains important notifications and pending join requests, suggested users, and seat upgrade requests, so admins can act on what needs attention, as well an at-a-glance overview of your organization stats, such as total users, apps, workflows, and AI credit usage.

BYOK AI token management

Retool introduced several features to help Enterprise organizations manage AI token spend when using their own API key for AI resources.

Use the new Get BYOK AI token usage endpoint to measure the number of tokens consumed for each AI resource that uses your own key. You can view the number of tokens consumed by resource, user, and surface area.

In addition, you can also view BYOK AI token usage in Settings. Navigate to the Usage Analytics page, and click the AI tab. You can filter AI usage by model, user, and feature.

Learn more about credit and token monitoring.

Object permissions

note

The object permissions feature is not yet available on self-hosted instances.

Retool now supports object roles—a new role type that grants groups Use, Edit, or Own access to specific apps, workflows, resources, and agents. Object roles are separate from organization roles, which control access to admin settings like billing and SSO.

When you create an object role, you set an access level for each object type and choose how the role applies:

  • Universal access—The role applies to all current and future objects of that type across the organization.
  • Individual access—Access is scoped to specific objects or folders, which you define when assigning the role to a group.

Object roles are assigned to groups from the Groups page. Once assigned, all members of the group inherit the role's permissions. You can view a group's or user's full object-level access from the Object permissions tab on their detail page in Settings.

Updates to organization roles​

As part of this launch, organization roles have been updated to cleanly separate admin settings access from object-level access. The Create Role button on the Roles & Permissions page is now a dropdown where you choose between creating an object role or an organization role. A filter control on the roles list lets you view all roles, object roles only, or organization roles only.

To get started:

  • Object roles—Understand how object roles work, including universal vs. individual access and folder inheritance.
  • Create an object role—Step-by-step instructions for creating and managing object roles.
  • Organization roles—Updated UI for managing organization roles, including a new role type selector and filter controls on the Roles & Permissions page.
  • Assign roles to groups—Assign object or organization roles to groups.