
Changelog

Updates, changes, and improvements at Retool.

Refer to the stable and edge release notes for detailed information about self-hosted releases.

5 posts tagged with "Business"

Updates related to functionality on the Business plan.

View All Tags

Custom authentication for embedded apps

Business and Enterprise organizations can now use the Retool API to authenticate apps that are embedded in an app or website external to Retool.

Once configured, the custom authentication flow exchanges an API token for an embed URL. When a parent app authenticates a user using your preferred authentication method, the parent app makes an API request to Retool to generate an embed URL. This embed URL is a secure, single-use link on the domain of your published app. Loading it in the iframe exchanges the link for a session, sets the cookies the app needs, and then displays the app.

Standard authentication through Retool remains supported.

note

This flow is available for apps published on a cloud instance that use the standard Retool domain (example.retool.com). It is not available to self-hosted instances or organizations that use a custom domain.
Object permissions

note

The object permissions feature is not yet available on self-hosted instances.

Retool now supports object roles—a new role type that grants groups Use, Edit, or Own access to specific apps, workflows, resources, and agents. Object roles are separate from organization roles, which control access to admin settings like billing and SSO.

When you create an object role, you set an access level for each object type and choose how the role applies:

  • Universal access—The role applies to all current and future objects of that type across the organization.
  • Individual access—Access is scoped to specific objects or folders, which you define when assigning the role to a group.

Object roles are assigned to groups from the Groups page. Once assigned, all members of the group inherit the role's permissions. You can view a group's or user's full object-level access from the Object permissions tab on their detail page in Settings.

Updates to organization roles​

As part of this launch, organization roles have been updated to cleanly separate admin settings access from object-level access. The Create Role button on the Roles & Permissions page is now a dropdown where you choose between creating an object role or an organization role. A filter control on the roles list lets you view all roles, object roles only, or organization roles only.

To get started:

  • Object roles—Understand how object roles work, including universal vs. individual access and folder inheritance.
  • Create an object role—Step-by-step instructions for creating and managing object roles.
  • Organization roles—Updated UI for managing organization roles, including a new role type selector and filter controls on the Roles & Permissions page.
  • Assign roles to groups—Assign object or organization roles to groups.

Purchase additional AI credits

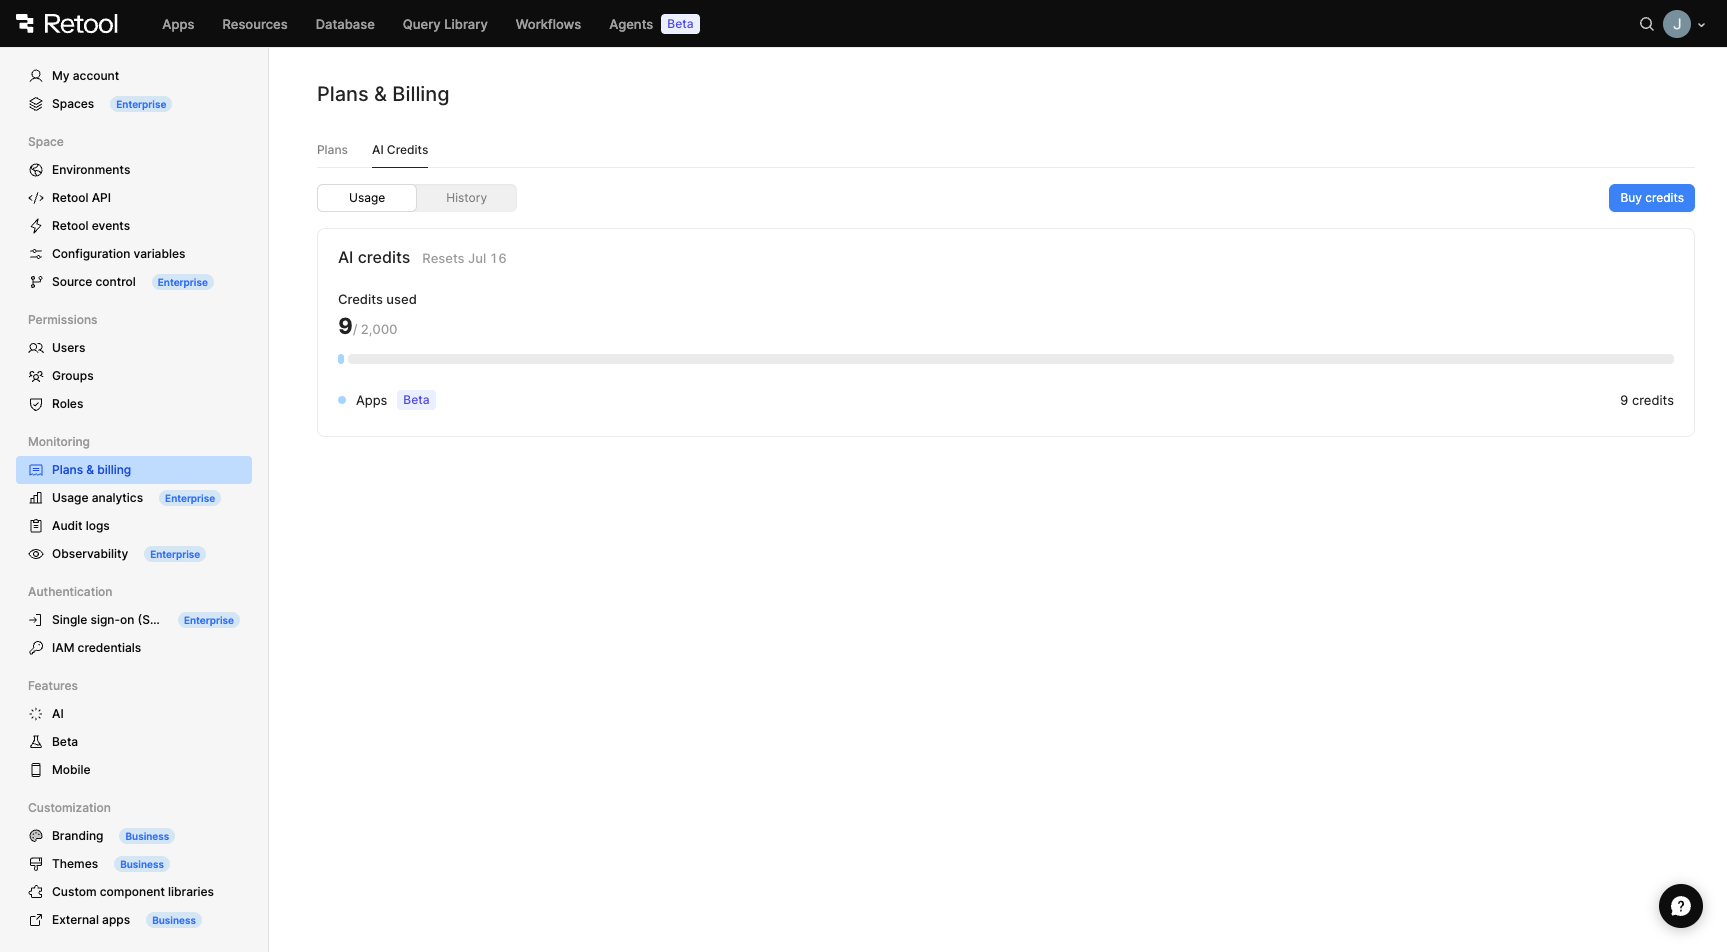
Organization admins on Team and Business plans can now purchase additional AI credit packs directly by clicking on Buy credits from Settings > Plans & Billing > under the new AI Credits tab.

AI Credits tab with Buy credits button

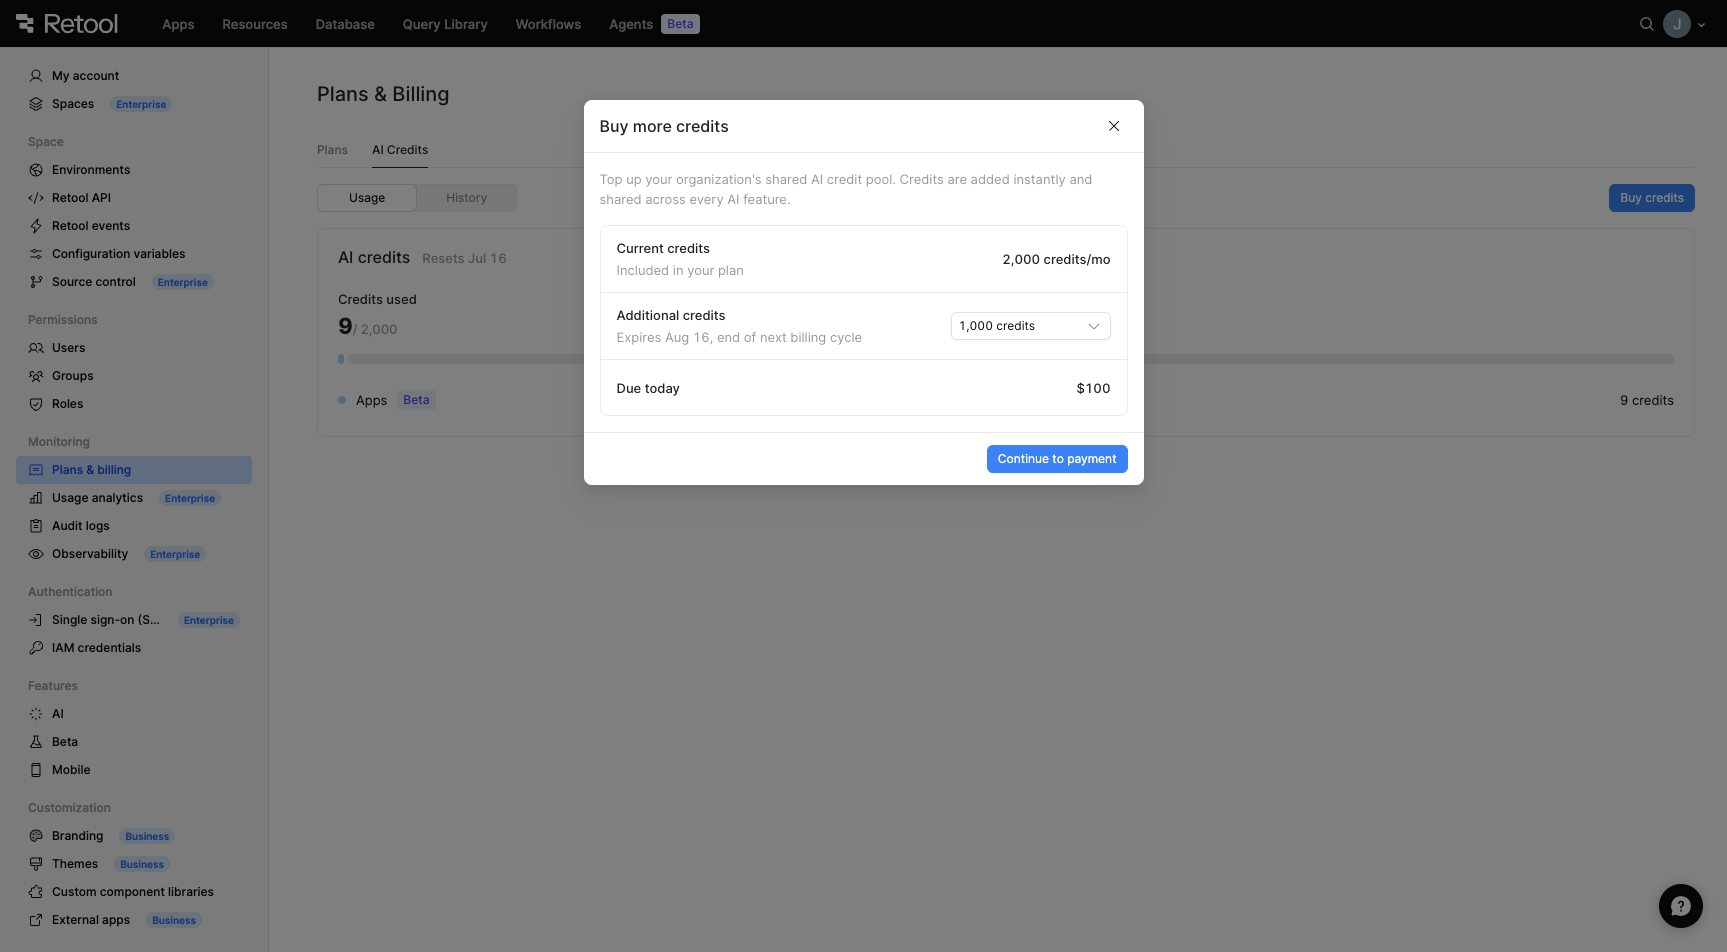
Credit packs are sold in increments of 1,000 credits at $100 per pack. Purchased credits are added to your organization's shared pool and are consumed after your monthly allotment runs out, with the oldest (soonest-expiring) pack used first. Credit packs expire at the end of your next monthly billing cycle (between 30–60 days after purchase), depending on where you are in your billing cycle when you buy them.

  • If you are billed monthly, your next billing cycle end date is your expiration date.
  • If you are billed annually, your monthly billing date is the same day of the month you originally purchased your plan (e.g., if you purchased an annual plan on April 12, credits expire on the 12th of the following month).

Buy more credits modal

When your organization's credits run out, admins will see a banner prompting them to purchase additional credits or upgrade their plan. Users who are not admins will be directed to contact their admin.

Credit pack purchasing is available on cloud plans using Retool-managed keys. Free plan organizations must upgrade to Team or Business to purchase credit packs. Enterprise customers should contact their account executive.

For more information, refer to the AI credits documentation.

Role-based access controls for Assist

For Enterprise and Business plans, Retool now allows admins to control access to Assist and its Ask and Build modes. Organization admins can use roles and permissions to create roles and edit roles with one of the following permissions:

  • Use Assist with Ask and Build mode
  • Use Assist with Ask mode only
  • No access to Assist

By default, all users have access to Assist and both Ask and Build mode through a preconfigured role. This role is called Assist Role or Editor, based on when your organization was created. Organization admins can edit these roles, or they can create new roles with more restrictive permissions.

This change is valuable for organizations that need to limit or prevent Assist usage to specific populations of users. For example, admins might wish to restrict Assist usage to user groups who do not have access to sensitive data or PII. Alternatively, admins could restrict access to all user groups except for a pilot group testing AI tools.

Update to default user permissions on Business and Enterprise plans

For new Business and Enterprise plan organizations, the All Users group does not have universal access permissions by default. Admin users can add permissions to the All Users group as needed.

This change was made to simplify the process of creating custom groups, eliminating the need to remove permissions from the All Users group before creating more permissioned groups.

This change does not impact existing organizations, or organizations upgrading from Free or Team plans.